
KaiwuDB PSIRT
KaiwuDB PSIRT (Product Security Incident Response Team) is KaiwuDB's product security incident response team, responsible for receiving, processing and disclosing security vulnerabilities related to KaiwuDB database products and solutions. It is the official channel through which KaiwuDB discloses vulnerability information.
The main responsibilities of KaiwuDB PSIRT include:
- - Formulate the company's security incident management policies and handling plans;
- - Analyze vulnerabilities and patches published by system software providers and professional security vendors;
- - Respond to and handle security incidents disclosed by customers, security organizations or individuals.
KaiwuDB Product Security Incident Response Team encourages security practitioners and industry organizations worldwide to proactively submit security vulnerabilities found in KaiwuDB products. KaiwuDB PSIRT follows ISO/IEC 30111 (Vulnerability Handling Processes) and ISO/IEC 29147 (Vulnerability Disclosure) standards, customized to the product characteristics of KaiwuDB multi-model time-series database, ensuring the entire process from vulnerability receipt, verification, fix to disclosure is standardized, transparent and efficient.
Email: security@kaiwudb.org.cn
1. How to Submit a Vulnerability
KaiwuDB PSIRT encourages global security practitioners and industry organizations to proactively submit security vulnerabilities found in KaiwuDB products, helping us continuously improve the security of KaiwuDB products and services. If you discover any security vulnerabilities, we welcome you to submit them promptly.
1.1Submission Channels
- -Dedicated Security Email: security@kaiwudb.org.cn
- -Customer Technical Support: Submit through your designated technical support channel with the label “Security Vulnerability”.
1.2Response Time Commitment
We will respond to all received security vulnerabilities at the earliest opportunity. Typically:
- -Within 1 business day — Email acknowledgment of receipt.
- -Within 7 business days — Verification conclusion provided.
- -Throughout the handling process, we will keep you informed of the latest progress.
1.3Submission Guidelines
To improve processing efficiency, please follow these guidelines when submitting vulnerability reports:
- -Use the report template to accurately and completely fill in vulnerability information.
- -Email subject format: [Product Name – Brief Vulnerability Description], e.g., [KaiwuDB – SQL Injection Vulnerability].
- -Ensure that the submitted report does not involve intellectual property issues and does not contain content prohibited by law or religion.
1.4Report Requirements
To facilitate verification and pinpointing of the vulnerability, the report should include a detailed description and a complete proof-of-concept (POC) code.
Report Description Requirements
- -Vulnerability Description: Describe the issue type (e.g., login bypass) and potential impact.
- -Affected Objects: Affected version numbers and specific functional modules where the issue occurs.
- -Reproduction Steps: Use text or screenshots to describe the operating environment and step-by-step actions to reproduce the issue. If convenient, attaching a video would be even clearer.
About Proof of Concept (POC)
If you have a runnable POC, please provide it along with the compilation environment details (e.g., compiler and operating system used).
1.5Confidentiality Commitment
Until KaiwuDB PSIRT makes an active public disclosure, we ask that you keep the vulnerability information confidential. Meanwhile, KaiwuDB PSIRT commits to keeping sensitive vulnerability-related information confidential on behalf of customers until the vulnerability is fixed and a security advisory is published.
For non-security-vulnerability-related issues, please contact global technical support.
2. PSIRT Core Process
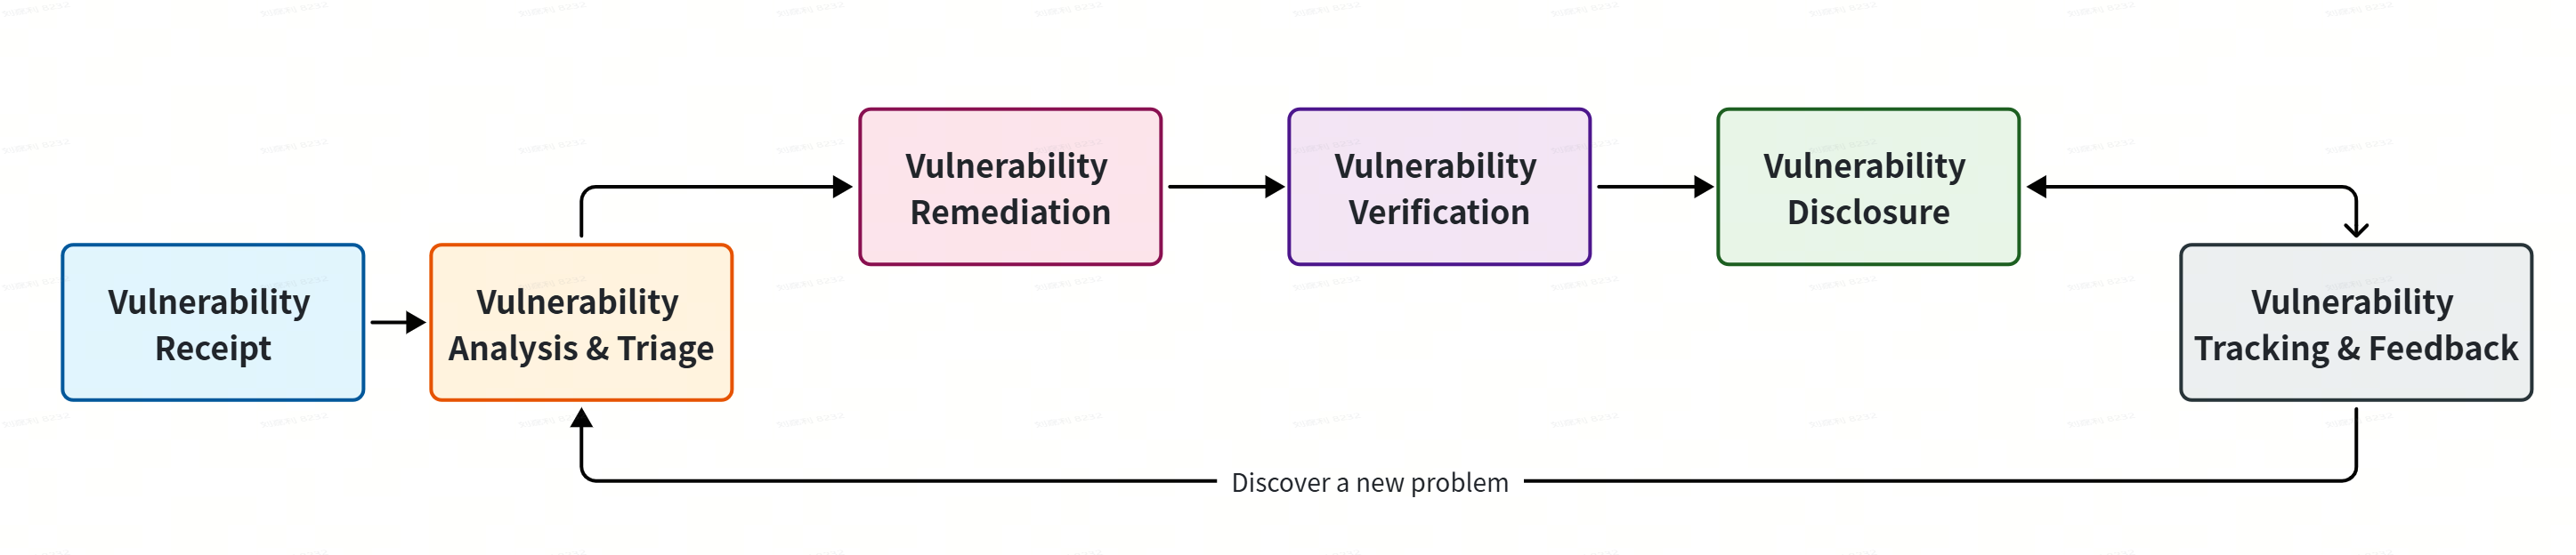
KaiwuDB PSIRT process consists of six phases: Vulnerability Receipt → Vulnerability Analysis & Triage → Vulnerability Remediation → Vulnerability Verification → Vulnerability Disclosure → Vulnerability Tracking & Feedback.
Phase 1: Vulnerability Receipt
Objective: Establish unified vulnerability receipt channels to ensure all security vulnerability reports are registered and acknowledged in a timely manner.
Receipt Channels
- -Dedicated security email: security@kaiwudb.org.cn
- -Public vulnerability database monitoring (CVE/CNVD/CNNVD/NVD).
- -Internal security testing and code audit findings.
- -Reports from third-party security organizations.
Receipt Handling Steps
- -Registration and Filing: Within 24 hours of receiving a vulnerability report, assign a unique vulnerability tracking number and record the source, date, product version, vulnerability description, and other information.
- -Acknowledgment: Send a confirmation receipt to the reporter, informing them that the vulnerability has been accepted and outlining the subsequent process, while establishing a communication channel.
- -Information Supplementation: If the report lacks sufficient information (e.g., reproduction steps, POC), proactively communicate with the reporter to obtain additional details.
- -Initial Triage: Filter out non-security issues, duplicate vulnerabilities, user configuration errors, and other reports that do not constitute product security vulnerabilities.
Phase 2: Vulnerability Analysis & Triage
Objective: Confirm the authenticity of the vulnerability, assess its impact scope and severity, and determine remediation priorities.
Analysis Contents
- -Vulnerability Verification: Reproduce the vulnerability in a test environment to confirm its existence.
- -Root Cause Analysis: Identify the underlying cause of the vulnerability (code defect, design flaw, configuration issue, etc.).
- -Impact Scope Assessment: Determine affected product versions, components, and deployment modes.
- -Severity Scoring: Apply CVSS scoring standards.
- -Exploitability Assessment: Evaluate the technical barriers and prerequisites for exploiting the vulnerability.
- -Business Impact Analysis: Assess the actual impact on customer business if the vulnerability is exploited.
Phase 3: Vulnerability Remediation
Objective: Develop security patches or provide mitigation measures to fundamentally eliminate security vulnerabilities.
Remediation Strategies
- -Develop Remediation Plan: The core R&D team formulates a code fix plan, and PSIRT reviews the plan for security and completeness.
- -Emergency Mitigation Measures: For high-severity vulnerabilities, provide temporary mitigation measures (e.g., configuration changes, access control policies, feature disabling) before the official patch is released.
- -Patch Development: The R&D team implements code modifications according to the remediation plan, following secure coding practices.
- -Multi-version Adaptation: Develop patches separately for all affected supported versions.
- -Remediation Self-Check: After development, perform unit testing and vulnerability reproduction verification.
Phase 4: Vulnerability Verification
Objective: Comprehensively verify the effectiveness, compatibility, and security of the patch, ensuring that the fix does not introduce new issues.
Phase 5: Vulnerability Disclosure
Objective: After the patch is ready, disclose vulnerability information to affected customers and the public through appropriate channels, providing remediation guidance.
Disclosure Principles
- -Responsible Disclosure: Disclose vulnerability details only after a patch or mitigation measures are available.
- -Tiered Disclosure: High-severity vulnerabilities are prioritized for notification to contracted customers; general vulnerabilities are disclosed via unified security advisories.
- -Sufficient Information: Advisories include vulnerability description, affected versions, risk assessment, remediation measures, and mitigation options.
- -Vulnerability Sources: Vulnerabilities submitted via email or collected from public information.
Disclosure Channels
- -Customer Priority Notification: For contracted customers, provide advance notice (48 hours) through technical support channels before public advisory release.
- -Official Security Advisory: Publish formal security announcements on the official Security Advisory page.
Phase 6: Vulnerability Tracking & Feedback
Objective: Monitor patch deployment, collect customer feedback, and continuously improve the security process.
Tracking Contents
- -Patch Deployment Monitoring: Track customer patch upgrade progress and identify high-risk customers who have not applied patches in a timely manner.
- -Issue Feedback Collection: Collect issues encountered by customers during patch application.
- -Vulnerability Exploit Monitoring: Monitor public channels for exploit code or in-the-wild exploitation intelligence.
- -Patch Updates: If patch defects are found, release revised patches promptly.
- -Root Cause Review: After high-severity vulnerability remediation is completed, organize a review meeting to analyze the root cause and formulate preventive measures.
- -Process Improvement: Translate review conclusions into secure coding standards, test cases, and automated detection rules.
3. Vulnerability Classification Standard
CVSS scoring system is adopted, combined with database business impact characteristics for classification.
4. Appendix
4.1Glossary
| Term | Full Name | Description |
|---|---|---|
| PSIRT | Product Security Incident Response Team | Product security incident response team |
| CVE | Common Vulnerabilities and Exposures | Common vulnerability disclosure identifier |
| CVSS | Common Vulnerability Scoring System | Common vulnerability scoring system |
| CVD | Coordinated Vulnerability Disclosure | Coordinated vulnerability disclosure |
| POC | Proof of Concept | Proof of concept; code or program used to verify the existence of a vulnerability |
| Exploit | — | Exploit program that can actually leverage the vulnerability to execute attacks |
4.2Reference Standards and Frameworks
- -ISO/IEC 30111:2019 — Information technology — Security techniques — Vulnerability handling processes
- -ISO/IEC 29147:2018 — Information technology — Security techniques — Vulnerability disclosure
- -FIRST CVD Guidelines — Coordinated Vulnerability Disclosure Guidelines
- -Regulations on the Management of Network Product Security Vulnerabilities — MIIT, CAC, MPS
- -CVSS Scoring Standards
4.3Version History
| Version | Date | Change Description |
|---|---|---|
| V1.0 | 2026-08-10 | Initial version release |